Queues for Jira & JSM
Organizes Jira and JSM issues from multiple projects into shared queues with access controls and queue management.
DevinitiFreemium
Records Jira changes with cryptographic signatures, hash chains, and RFC 3161 timestamps.
Records Jira changes using cryptographic signatures and hash chains. It adds RFC 3161 timestamps and supports independent verification of the resulting audit log.
Signs Jira changes cryptographically.
Links Jira changes through hash chains.
Applies RFC 3161 timestamps to Jira changes.
Supports independent verification of Jira changes.
382 plugins in Jira · Security and compliance
Price distribution: 154 free, 73 freemium, 155 paid
Organizes Jira and JSM issues from multiple projects into shared queues with access controls and queue management.
Deviniti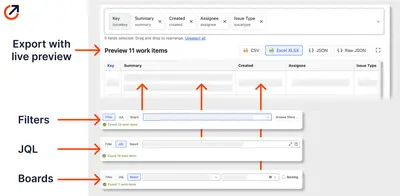
Scheduled Jira exports create reports with custom fields, change history, and delivery by email, SFTP, download link, or API.
Advanced Insights
Embed shared Microsoft Power BI links in Jira issue tabs and dashboards with notes, images, PDFs, and other apps.
Apps+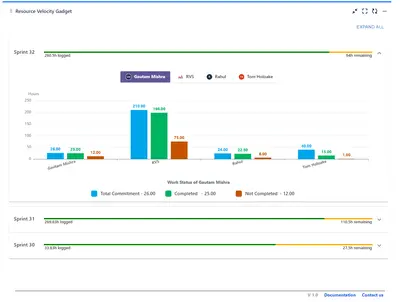
Track sprint progress and team velocity in Jira with dashboard gadgets, charts, and status views.
RVS Softek«Every Jira change cryptographically signed, hash-chained, RFC 3161 timestamped — tamper-evident and independently verifiable»